
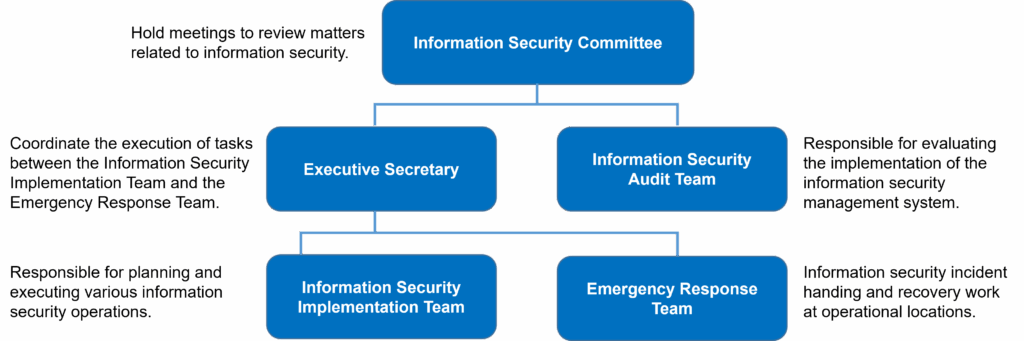

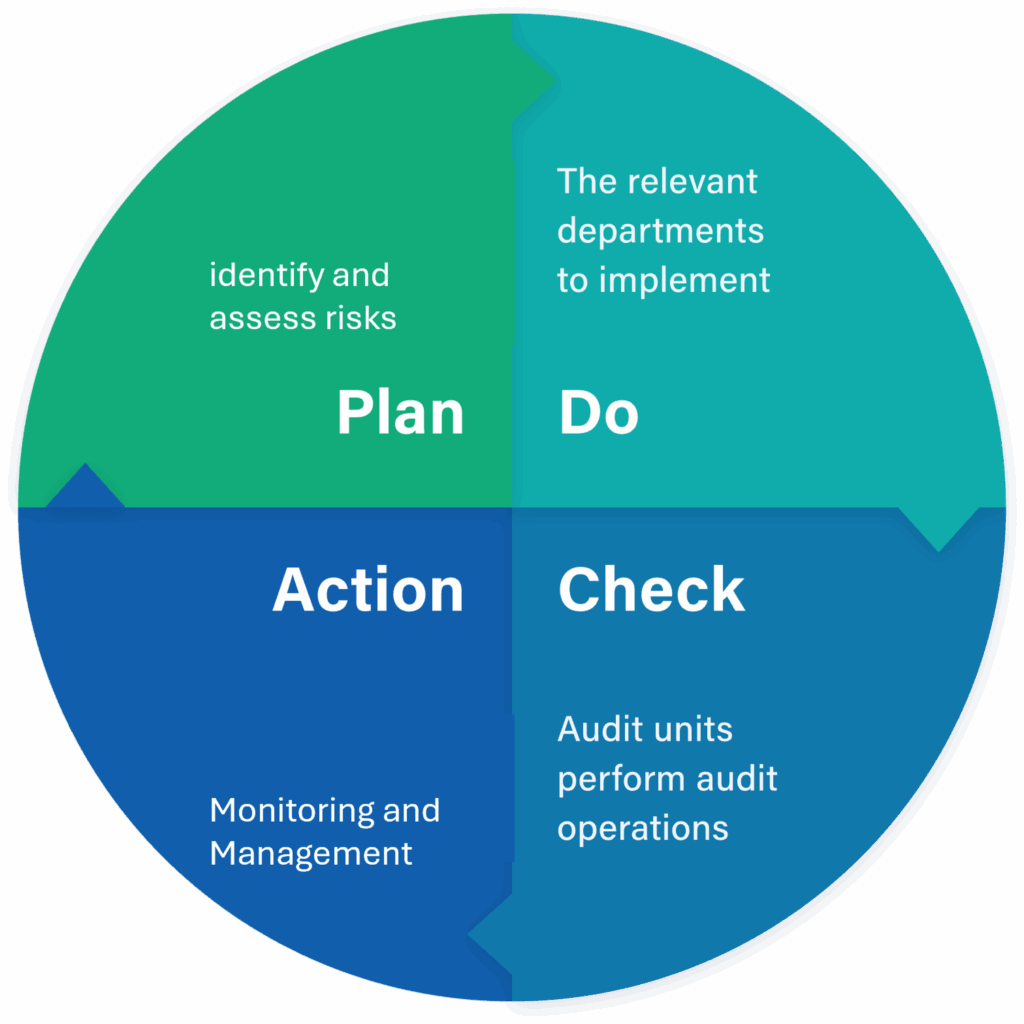
Specific management plans and resources devoted to cyber security management
The Company focuses on cyber security control, and the specific measures adopted are mainly based on five aspects of cyber security management:
01
Employee Management
At the time of employment, the Company signs a “contract of employment” with the employee, which stipulates that the intellectual property rights of all creations and inventions made by the employee during the employment period shall be vested in the Company. At the same time, the Company signs a detailed “confidentiality agreement” with the employee, which stipulates that the employee is responsible for maintaining the confidentiality of all business information, technology, processes, programs, procedures, designs or any other confidential information that the employee may use in the design, sale or operation of the Company, whether during or after the termination of the employment contract. The Company may impose penalties in accordance with its work rules for any breach of contract.
In case of contract violation, the Company may impose penalties in accordance with the work rules and, depending on the seriousness of the situation, may pursue criminal liability. The Company uses various meetings to educate employees from time to time, including the protection of business secrets, access control rules, and the principle of disclosing information to the outside world, etc., so that employees can establish correct concepts and develop good working habits.
02
Device Control
The Company’s computer equipment must be installed with antivirus software. The system will determine that the computer meets the specifications before granting network connection authorization. Any unauthorized computer equipment is strictly prohibited from accessing the Company’s network, and the system will automatically block any unauthorized equipment to prevent non-compliant computer devices from affecting the Company’s internal network and equipment.
03
Access Management
To avoid theft and fraudulent use of accounts, Company employees are required to pass two-factor authentication (system account password + OTP one-time password) to access their personal computers. Each R&D project has strict permission control. Project members are required to submit a form to apply for access privileges. The information management staff will set the access privileges after the supervisor’s approval. Access privileges are reviewed once every six months to ensure the correctness of privilege management.
04
Data Management
The Company’s R&D-related data are stored in dedicated storage devices with high-availability redundancy, and project R&D data are controlled by privileges, allowing only authorized members to access them. The Company’s R&D data has a complete regular backup mechanism and is stored off-site to ensure disaster recovery capability in the event of a disaster.
05
Release Management
When the product is delivered to the customer, the application must be completed. The data will be encrypted by the system and uploaded directly to the dedicated space provided by the Company to the customer for downloading without the intervention of anyone in the industry. This dedicated space only allows the specific IP device connection provided by the customer. The connection opening time is limited to one month.
| Type | Item | Prevention Purpose | Information Security Management Resources Description |
| Employee Management | Information security advocacy | Prevention reduces the chance of getting a virus | Information security advocacy for new hires Regularly share cases of major domestic and international information security abnormalities with employees |
| Device Control | Antivirus software Untrusted device blocking |
Prevention of software virus | Information Security System Procurement and Implementation The system determines that the computer meets the criteria before granting permission to connect to the network. If there is an unauthorized device accessing the system, the network will be blocked. |
| Access Management | Two-factor authentication Project authority control |
Avoid account impersonation |
Two-factor authentication system setup Internal R&D management system development |
| Data Management | Professional Storage Equipment Local redundancy architecture Off-site data backup |
Avoid Data loss |
Professional Storage Equipment Procurement Professional Backup Software Procurement |
| Release Management | Automated system rotation Dedicated encryption space |
Avoid Data breach | Internal shipment management system development When the product is delivered to the customer, an application form is required. After the approval of the relevant supervisor and sales contractor, the system will encrypt the data and upload it directly to the exclusive space provided by the Company for the customer to download without any manual intervention. Exclusive space allows only certain IP devices provided by customers to connect. |
Cyber Security Management Execution Overview
On August 5, 2026 the Board of Directors reported the following executive highlights for the year:
| Item | Execution Details | Execution Results |
ERP Server Database Version Upgrade | The previous ERP server version was outdated, leaving no available patches for newly discovered high-risk vulnerabilities. After upgrading the database version, high-risk vulnerabilities can now be patched promptly, reducing potential cybersecurity risks. | Upgraded to the latest version, ensuring vulnerabilities can be patched on the server in a timely manner. |
MOTP Two-Factor Authentication System Upgrade | The previously used MOTP two-factor authentication system was facing end-of-update status. After negotiating a preferential upgrade price with the vendor, the new system adopts FIDO passwordless login, making account verification more secure and convenient. | Two-factor authentication now uses the latest encryption algorithms and push notification features, significantly improving both security and user convenience. |
EDR Endpoint Detection and Response System Deployment | To enhance the company’s information security management capabilities, critical servers have been enrolled in the EDR endpoint system for 24-hour monitoring, ensuring that anomalous events outside of working hours are handled immediately. EDR is a proactive cybersecurity solution that installs agents on endpoint devices (computers, servers, mobile devices) to continuously monitor abnormal behavior and suspicious activities, offering superior protection compared to traditional antivirus software. | All critical servers are monitored 24/7 by an external cybersecurity team. Any anomalies are reported and addressed immediately. |
Social Engineering Drill | A social engineering drill was conducted in Q4 2025. A total of 388 emails were sent, with an overall employee pass rate of 92.78%. Following the drill, a phishing email response notice was distributed, and information security policies were promoted on the company intranet to raise security awareness among all employees. | Enhanced employees’ ability to respond to phishing emails. No major cybersecurity incidents have occurred to date. |